
Most companies know they have AI exposure.
We source the talent to close the gap.
Whether you need a senior leader to own your AI governance, risk, and compliance function or a specialist within one of these domains, we find professionals who have done the work.
The reason your requisition isn't working
Three years ago most of these jobs did not exist. The work has since pulled people out of security, privacy, legal, audit and model risk — each arriving with its own established vocabulary. Plenty of companies have defined these roles clearly for themselves. What almost nobody has is a map that translates between them.
That matters more than it sounds. A requisition written in one company's vocabulary still has to reach candidates who describe the same work in another's. Where that translation is missing, the post goes up anyway — and the pipeline fills with privacy generalists and security engineers who have never been near a model. Ninety days later the role is still open and the audit date has not moved.
We did not invent these categories. NIST's AI Risk Management Framework, ISO/IEC 42001, ISO/IEC 23894 and the IAPP already define the work. What none of them settle is whether it is one hire or four, what to title them, what each one costs, or which adjacent backgrounds actually convert — the IAPP's own profession research finds no clear best practice for how these teams get built. That hiring layer is what we built: eight domains, the boundary lines between them, and what each one is worth. It sits behind every search we run. If your team already has it mapped, say so on the first call and we will work from your definitions rather than ours.
A thin market, and thinner than the headline number
Roughly four thousand people worldwide hold the field's anchor credential. More than fourteen thousand US roles are open against it. The gap is the whole business case for a specialist.
AIGP figure recurs across sources but is not published by IAPP directly — treat as directional. Certification is not the only qualification; the true practitioner pool is larger. It remains thin by any measure.
These roles get created for two completely different reasons
Same titles on paper. Different budget holder, different urgency, different definition of a good hire. Most search firms only notice the first one.
The enterprise deploying AI
Hires to stay out of trouble. The trigger is an audit finding, a board question, a customer's vendor questionnaire, or a state statute with a date attached to it.
This buyer usually knows they have exposure and does not yet know what to call the person who fixes it. Half of the work is translating a risk problem into a role definition, a comp band, and three names worth talking to.
The AI vendor selling into that enterprise
An AI vendor's deal rarely dies in the product evaluation. It dies in the security review that comes afterward. Someone has to own that room, and increasingly that someone is a dedicated hire.
The clearest expression is the Field CISO — a role that runs no internal security operations at all. It exists to enable sales, and it is measured the way sales is measured: pipeline, deal velocity, win rate. It is a revenue function wearing a security title.
Eight domains. Every seniority level inside each one.
Clients frequently arrive describing a single hire, defined by a title. Titles travel badly between companies — the domain and the level underneath are what actually determine who fits.
Governance
Policy, program ownership and the approval gate for how AI gets built and shipped. Runs from analyst to Chief AI Officer.
Risk
Model risk management and enterprise AI risk assessment. Strong overlap with banking model risk, at every level.
Compliance
Regulatory readiness against the state patchwork and customer contracts. IC through compliance executive.
Audit & Assurance
Independent testing and attestation that controls actually work. The function this practice is named for.
Privacy
Privacy engineering and data protection inside ML systems. Blends engineering, law and model design.
Security
ML security, LLM security architecture and AI red teaming. Prices against security bands, not compliance.
Safety & Trust
Trust and safety, bias mitigation, alignment. Concentrated at frontier labs, with bias mitigation the enterprise crossover.
Data Governance
Provenance, lineage and stewardship of training data. Upstream of every other function on this map.
The forcing function isn't one law. It's liability.
There is no single American statute playing the role the EU AI Act plays in Europe. What exists instead is a live state patchwork — Texas's TRAIGA and California's SB 53 and AB 2013 all in force since January 2026, Colorado's original framework repealed and rewritten — layered under a federal effort to preempt state AI law entirely.
Betting a hiring thesis on any one of those surviving would be foolish. The durable driver sits underneath all of it: enforcement under laws that already exist. Thirty documented federal AI enforcement actions as of July 2026 across the FTC, SEC, DOJ, EEOC and FCC. A $17M FTC settlement over deceptive AI claims. Active EEOC pursuit of AI-driven hiring discrimination under Title VII. D&O policies beginning to carve out AI exposure.
That is board-level liability, and it does not depend on one bill surviving one political fight.
Eleven years hiring into AI companies, before it was a category
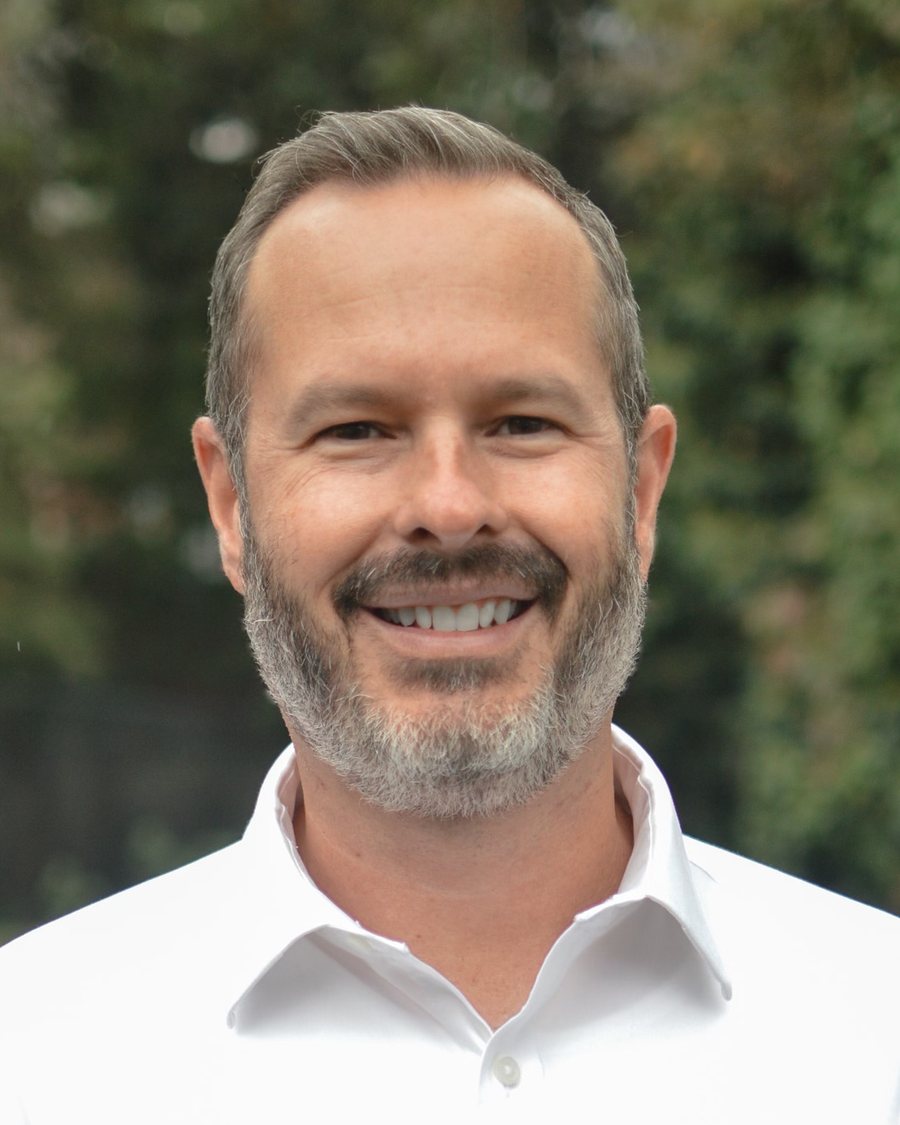
I have spent eleven years building go-to-market teams for AI startups — US and international — including one working on agentic systems well before anyone had a name for that. Most of that time was spent on the hidden market: the people who are good enough that they are never actually on the market.
Some of that work put me in the middle of enterprise security reviews, coordinating between our engineers and the security teams at brands like Cigna, Amazon, Meta and Omnicom. Often the pilots went well and the relationships were heading toward enterprise licenses until they stalled — not because we could not answer the questions, but because we lacked the talent who understood these were non-negotiable and could actually execute a plan to address each item while the deal was still live.
That skill transfers directly, because this is a passive-talent problem before it is anything else. Four thousand credential holders worldwide. The strong ones are employed, well paid, and not reading job boards.
So I am building this market map candidate-first, function by function — published where it is useful to the field, proprietary where it took real work. You will not be handed to an account manager. Every search on this site is one I run personally.
Questions we get every week
AI governance is the internal system that decides how AI gets built and shipped — who approves a model, what testing it has to survive, who is accountable when it misbehaves. AI compliance is the narrower job of proving that system satisfies an external rule: a state statute, a customer contract, an auditor's request.
Governance is the machine. Compliance is the receipt. Companies routinely hire for the second when the problem is the first, which is how you end up with a compliance manager who has no authority to stop a launch.
It's the umbrella term for independent testing, attestation and ongoing verification of an AI system — proving it does what it should and does not do what it shouldn't, on a continuing basis rather than a one-time sign-off. It sits across governance, risk, compliance and security rather than belonging to any one of them alone.
Almost nobody in the US hires under that title yet. The work gets done by auditors, compliance managers, risk analysts and security engineers, each holding one slice of it — which is the gap this practice is built to translate.

Tell us what broke, and we'll tell you what to hire.
Whether that turns into a search is a second conversation. The first one is free and usually saves a quarter.